
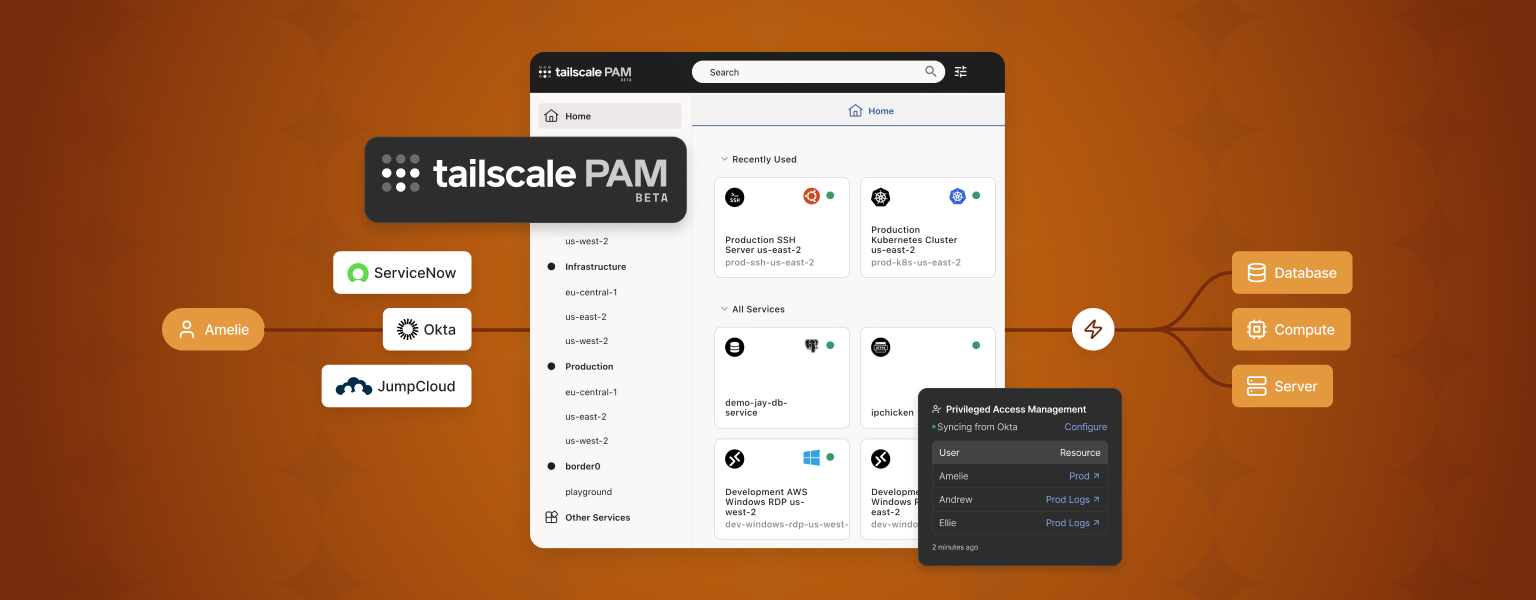
Where Tailscale VPN ends and Tailscale PAM begins
AI Summary
This article explains the differences and relationship between Tailscale VPN and Tailscale PAM (Privileged Access Management). While Tailscale VPN creates a peer-to-peer mesh overlay network to secure connections between users, devices, and apps, Tailscale PAM provides infrastructure access administration, credential injection, and detailed logging for services like databases, SSH, Kubernetes, and web apps. Using PAM connectors, administrators can enforce the principle of least privilege without needing to install the Tailscale client on every backend server.
Key Takeaways
- Tailscale VPN builds a peer-to-peer mesh overlay network (tailnet) using WireGuard.
- Tailscale PAM utilizes PAM connectors deployed on the local network to mediate access to services like databases and Kubernetes without installing client software on every target server.
- PAM eliminates shared credentials through automatic credential injection and provides detailed audit logs, including query logs and SSH video replays.
Why it matters
Understanding the distinction between network-layer VPN connectivity and application-layer privileged access management helps engineering teams secure internal infrastructure, eliminate shared long-lived credentials, and improve auditability through robust session recording.
Conversation 0
Be the first to share your perspective.